Trust centre
Can you stand behind the numbers?
Sending your plans to someone else lives or dies on that question. This page explains how we make a schedule, who signs it off, how we handle your plans and pricing, and how we secure them.
The Estimates service runs on TakeoffQS software, so the data handling and security below are the same ones that cover the software.
01How a schedule gets made
Our engine does the takeoff and marks every measurement up on the drawing. Then an experienced QS or estimator checks it before anything goes back to you.
The models find things. The geometry computes things.
Detection is the part that can be wrong, and it's the part a person can see and check right on the plan. Once an element is confirmed, its length or area comes from arithmetic, so every quantity traces back to something visible on the drawing. A model asked to output the number directly can't offer that trail.
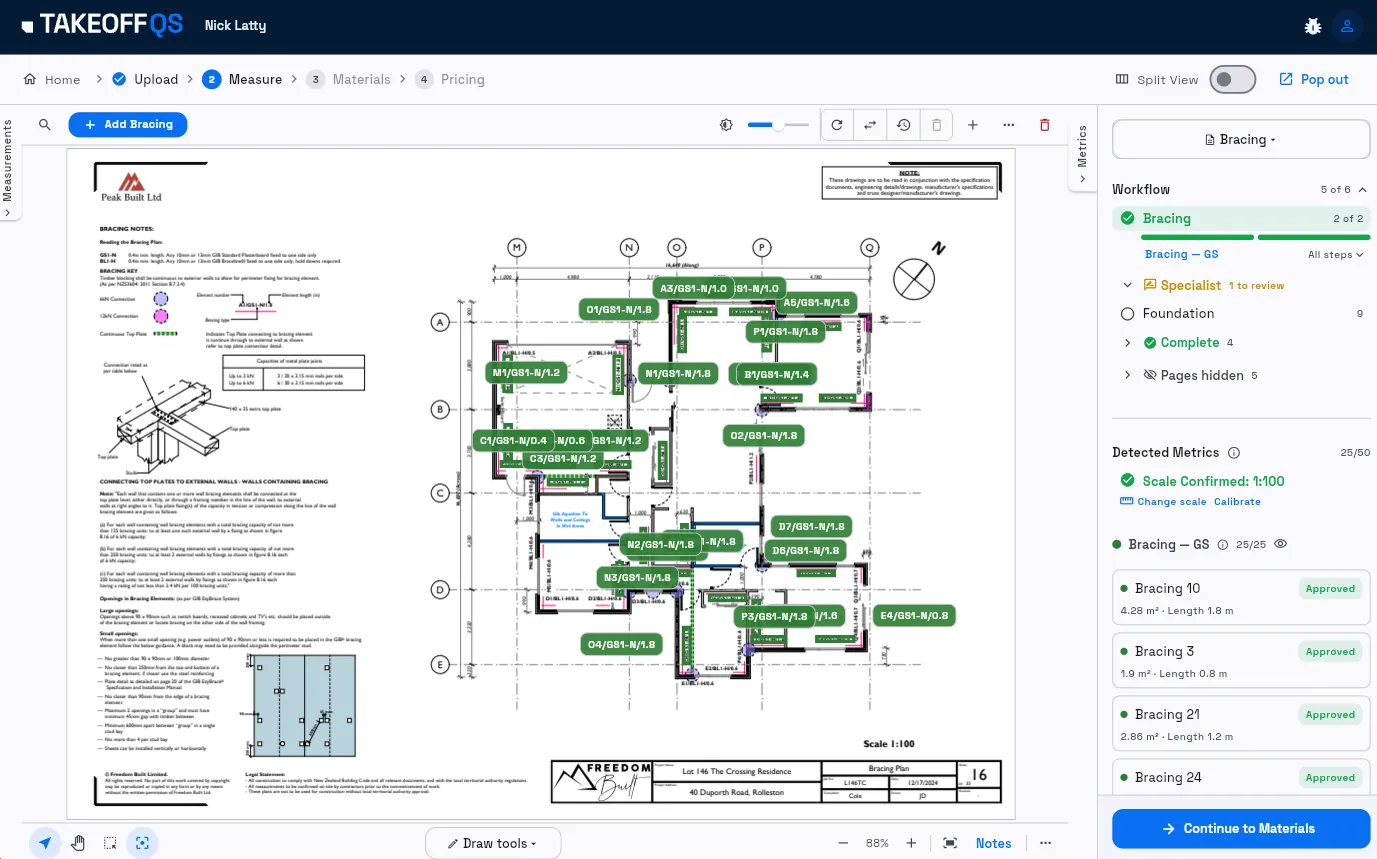
We deliberately don't hand the whole plan to a large language AI model (like ChatGPT, Claude or Gemini) and ask for a takeoff. The failure mode of that approach is confident, plausible, wrong numbers with no traceable origin. We do use models like these for narrow, checked reading tasks inside the pipeline, and they are named in our subprocessor list. What we don't do is ask one for the number.
The full technical breakdown is in The AI models behind TakeoffQS.
02A person signs off every schedule
No schedule goes out until an experienced QS or estimator has checked it and signed it off. Every schedule comes with a numbered list of what we assumed, what we left out and anything we couldn't resolve, so your team can follow our working.
So the split is explicit
We measure and check. Your estimator checks it again before you quote or order, sets the order quantities and owns the quote.
If we measured, calculated or mapped a product code wrong, tell us and we fix it free, whenever you find it.
You'll notice we don't publish a single accuracy percentage. One number can't describe performance across every plan style, page type and scope, and a number that can't be trusted everywhere shouldn't be published anywhere.
Here's what we will say. Once the drawing scale is calibrated, measurement is arithmetic. The length of a confirmed annotation on a correctly scaled plan is the length; the numbers are what they are. The uncertainty lives in detection (did we find every wall?) and interpretation, which is exactly what the sign-off covers.
03What a schedule isn't
A schedule is not:
- A purchase order Every schedule is an estimate. Your estimator checks it and sets the order quantities.
- An engineering certification
- A compliance statement
- A bracing calculation We detect and read bracing annotations on the plan, we don't calculate bracing adequacy.
- A design check We don't check your plans for design errors, though we'll flag anything obvious.
- A finished quote to send a builder as it stands What a builder gets from you is your quote, based on quantities your team has checked.
Results also depend on the plans. Clean, complete drawings get better first drafts than scanned, partial or heavily revised ones. That's why we ask for complete, current plans.
04Your data
Your plans, product list and pricing stay confidential. Three things worth saying plainly.
Your plans and corrections train our models
We use the plans and corrections you send to run and improve the service, including training our own measurement models. It's how the engine gets better on NZ plans.
Your commercial data never does
Pricing, catalogues, margins, quote values: none of it is used to train anything. Nothing that identifies you, your pricing or your customers goes to any other customer.
No third party trains on your data, ever
Our AI subprocessors are not authorised to use client data for model training, and that is a contractual term, not a preference. Through the first half of 2026 we moved model training in-house, onto our own infrastructure, so the training corpus and every model checkpoint sit in our own storage.
Our full subprocessor list, with regions and the categories of data each one touches, is available on request: email privacy@takeoffqs.com. We give clients 30 days' notice before adding to it.
05Security
Inside TakeoffQS, your data is stored in Google Cloud's Sydney region (australia-southeast1): the application, the database and file storage. Nothing at rest leaves Australia.
AI inference is the exception, and we'd rather say it than have you find it. Drawing content is sent to our AI providers for inference. Where that processing happens varies and can be anywhere in the world, under enterprise terms that give them no right to train on it. Storage never moves: nothing at rest leaves Australia.
Tenant isolation is enforced in the database
Queries run behind Postgres row-level security scoped to your organisation. It's a database rule, and our CI blocks changes that would weaken it.
No static database passwords exist
Services authenticate to the database with short-lived Google IAM credentials. Secrets live in Google Secret Manager, scoped to the specific services that need them.
Your files are private
Storage buckets have public access prevention enforced. Plan downloads use short-lived signed URLs.
Backups run continuously
Point-in-time recovery covers the last 7 days, encrypted at rest. Our disaster recovery plan commits to a full restore test at least annually.
Logs are scrubbed
Email addresses, long digit strings and credential-shaped values are redacted before anything reaches our logging systems.
We're working toward SOC 2 and ISO 27001 certification now. Until they're done, the controls above are the honest answer to the security questionnaire, and we're glad to walk your IT team through any of them.
Incident response
We have a documented incident response process with severity levels, a 1-hour triage target and breach notification obligations under the NZ Privacy Act 2020 built into our standard agreement.
06Questions
If your IT or procurement team has a security questionnaire, send it over. We'd rather answer it properly than have you guess. Email privacy@takeoffqs.com and it lands with our CTO.
For how the service runs day to day (getting started, turnaround, fixing errors and fees), see How we work.